The best Active Directory practices come down to five jobs: shrink and protect the accounts with admin power, set a modern password policy, lock down domain controllers, keep Group Policy clean, and govern who has access in Microsoft 365. They are not a one-time setup. Access piles up, settings drift and attackers go after admin accounts first, so the routine matters more than any single setting. At Axio Networks we run this routine for Phoenix-area businesses as part of managed IT with security built in, so owners without an IT department are not left carrying it.
TL;DR
- Protect the three highest-privilege groups (Enterprise Admins, Domain Admins, Administrators) and give admins separate accounts, MFA and dedicated admin workstations.
- For cloud accounts in Microsoft 365, Microsoft recommends a 14-character minimum and MFA, with no forced periodic expiry.
- Keep domain controllers physically secure and apply security baselines through Group Policy.
- Remove old risks: LLMNR, open admin shares and stored passwords in Group Policy files.
- Review who has access on a schedule, because people collect permissions as they change roles.
Table of Contents
- What Active Directory is and why it matters to a small business
- 1. Protect the accounts with the most power
- 2. Set a password policy that fits how attackers really work
- 3. Harden the domain controllers
- 4. Keep Group Policy clean and purposeful
- 5. Switch off legacy settings attackers rely on
- 6. Govern Microsoft 365 and Entra ID, not just the server
- A sensible order of work
- Where managed IT fits
- Our perspective
- FAQ
- Sources
What Active Directory is and why it matters to a small business
Active Directory (AD) is the directory service on a Windows server that keeps the list of your users, computers and groups, and decides who can sign in and open what. A domain controller is the server that holds that directory and answers every sign-in request. If you have a file server, shared drives, Windows PCs joined to a company domain or a login that works across several machines, you probably have AD.
Most small businesses today run a mix: AD on a server in the office, plus Microsoft Entra ID (the cloud directory behind Microsoft 365, formerly called Azure AD). Our guide on Microsoft Entra ID and why it matters for your business explains the cloud side. The practices below cover both, because an attacker who owns one often reaches the other.
The reason AD gets so much attention is simple. It is the master key ring. Whoever controls it can create accounts, change permissions, reach critical data and stay hidden for months. Everything in this article reduces the chance that one stolen password becomes control of the whole network.
1. Protect the accounts with the most power
Start here, because it removes the most risk for the least effort. Microsoft names Enterprise Admins, Domain Admins and Administrators as the three built-in groups with the highest privileges by default and tells administrators to take deliberate steps to protect them.
In practice for a 20 to 200 person company:
- Keep the groups small. Most businesses need two or three people in Domain Admins, not ten. Every extra member is another password an attacker can phish.
- Separate daily and admin accounts. The person who reads email and browses the web should not do it while signed in as a domain administrator. Give admins a second account used only for admin tasks.
- Use least privilege. Microsoft’s guidance on Entra roles describes it as granting exactly the permission needed, over a specific scope, for a specific period. Its recommendation is just-in-time access through Privileged Identity Management: a person is eligible for a role, activates it for a limited time, and the access is removed automatically when time runs out.
- Use dedicated admin workstations with MFA. Canada’s cyber agency advises that administrators use dedicated administrative workstations with hardware-token multi-factor authentication for all administrative tasks. Multi-factor authentication (MFA) means a password plus a second proof, such as a security key. Our piece on why MFA protects your accounts covers the basics.
The Australian Signals Directorate goes further for the most sensitive accounts, recommending phishing-resistant MFA and Kerberos armoring as protections for Tier 0. Tier 0 means the identities and servers that control everything else, chiefly domain controllers and domain admin accounts. Kerberos is the sign-in protocol AD uses, and armoring wraps its exchanges in extra protection.
Microsoft stresses that Tier 0 containment is a boundary defined by the account and the host used, not by network segmentation alone. In plain terms: a domain admin must never sign in to an ordinary employee PC, because that is where stolen credentials are collected.
2. Set a password policy that fits how attackers really work
Password policy is the most searched part of this topic, and the advice has changed. Forcing everyone to pick a new password every 60 days tends to produce Summer2026! followed by Fall2026!. For cloud-only accounts in Microsoft 365, Microsoft recommends passwords that never expire, a 14-character minimum, MFA registration and identity protection risk policies.
A workable policy for a small business looks like this:
- Length over complexity. Require at least 14 characters and encourage passphrases of several unrelated words.
- Turn on MFA for everyone, not only admins. A stolen password alone then no longer opens the door.
- Block weak and leaked passwords. Microsoft recommends deploying self-service password reset (SSPR) and password protection to eliminate weak passwords, and notes that password hash sync can give insight into leaked passwords. SSPR lets staff reset their own password, which also cuts help desk calls.
- Give people a password manager so long, unique passwords are realistic. See our guides to creating and managing strong passwords and managing work and personal passwords.
- Change a password when there is a reason, such as a suspected breach or a departing employee, not on a calendar.
One caution on scope: the never-expire recommendation is written for cloud-only accounts. Accounts that still live in an on-premises domain may be governed by older policies and by compliance rules that apply to your industry, so check those before changing anything.
3. Harden the domain controllers
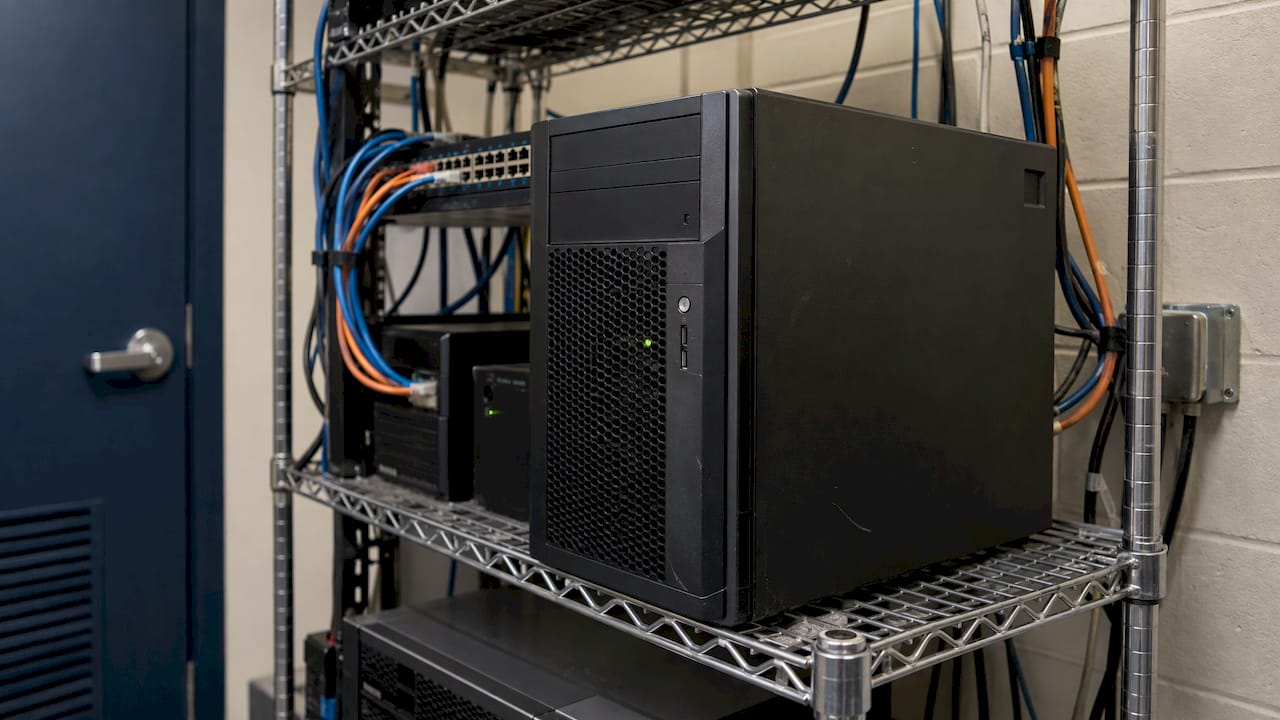
Domain controllers deserve stricter treatment than any other server you own. Microsoft’s guidance is to keep them physically secure and configured with security baselines enforced through Group Policy Objects. For an office, that means the server sits in a locked room or a managed data center, not under a desk.
Beyond the lock on the door:
- Run only what a domain controller needs. No email, no web browsing, no shared apps on the same machine.
- Keep it patched and monitored. An unwatched domain controller is how a quiet intrusion goes unnoticed for weeks.
- Keep tested, off-site backups. If AD is damaged or encrypted by ransomware, restoring it cleanly is the difference between a bad day and a bad month. Our guide to building a backup and disaster recovery plan walks through the planning.
If you do not want a physical domain controller at all, moving workloads to the cloud is a legitimate option. We handle that through cloud migration and management.
4. Keep Group Policy clean and purposeful
Group Policy is how you push settings to every computer and user at once: screen lock times, USB rules, firewall settings, software restrictions. It is powerful, which is why a messy Group Policy is a risk as well as a nuisance.
Good habits:
- Start from a baseline, not a blank page. Microsoft’s Security Compliance Toolkit provides preconfigured GPO baselines that you can compare against your current environment to spot deviations.
- Treat baselines as a starting point. Microsoft’s own product teams say a baseline is where you begin, then balance hardening against what your staff need to do their jobs. A policy that blocks the accounting software helps nobody.
- Test before you roll out. Apply a change to a small pilot group of PCs first, then widen it.
- Name and document each policy. Write down what it does and why. Policies nobody understands never get removed.
- Remove stored passwords. CISA recommends auditing SYSVOL and deleting Group Policy Preferences XML files that contain credentials, since they are exposed if AD is ever compromised. SYSVOL is the shared folder on domain controllers where Group Policy files are kept.
On the endpoint side, our overview of endpoint hardening shows how these settings fit with the rest of device protection.
5. Switch off legacy settings attackers rely on
Older networks carry old defaults that made sense in 2005. Three are worth a look, and all can be handled through Group Policy:
| Setting | What the risk is | What CISA recommends |
|---|---|---|
| LLMNR (Link-Local Multicast Name Resolution) | An old name lookup method that lets an attacker on the network capture credentials | Disable it via GPO to disrupt man-in-the-middle attacks and credential harvesting |
| Administrative and hidden shares | Let an attacker move from one PC to another | Disable them on endpoints, and where risks permit consider isolating TCP port 445 between workstations |
| File Replication Service (FRS) | Deprecated method of replicating SYSVOL | Migrate to DFSR, the Distributed File System Replication service |
Test each change first. Turning off a share that an old scanner or backup job quietly depends on will cause a support call, so make the change in a pilot group and watch.
6. Govern Microsoft 365 and Entra ID, not just the server
For most small businesses, the identity that matters most now sits in Microsoft 365. Searches for “Microsoft 365 governance” and “M365 tenant management” are asking the same thing: who has access to what, and can we prove it?
Microsoft’s guidance is to follow Zero Trust: verify identities with strong authentication, apply least-privilege access, and assume a breach so the damage from one stolen account stays small. That applies to cloud-only and hybrid setups alike.
The everyday governance tasks are modest:
- Review access on a schedule. Microsoft’s Entra ID Governance guide notes that users accumulate access as they move through teams and positions, so regular reviews are essential. Pick a quarterly date and review who is in which group, who has admin roles and which outside guests still have access.
- Automate joiners and leavers. Entra ID Governance supports lifecycle workflows and entitlement management that add and remove people from groups when their role changes. Even without automation, keep a written offboarding checklist and run it the day someone leaves.
- Assign owners. Every group, shared mailbox and app should have a named person responsible for it.
- Watch admin roles closely. The same Microsoft guide notes that attackers target admin accounts to reach sensitive data quickly, which is why just-in-time admin access and regular admin reviews matter.
- Lock down email sign-in. Our authentication checklist for Microsoft 365 email security covers the three controls to set first.
U.S. guidance has also moved recently. CISA published version 2.0 of its Entra ID Secure Configuration Baseline checklist on October 26, 2026, with specific policies for securing Entra ID. On the on-premises side, DISA published Active Directory Forest STIG version 3 release 2 on September 14, 2026. It was written for Department of Defense systems, but it is a detailed reference for settings that matter to any AD environment, and especially useful if you work as a defense contractor.
A sensible order of work
If you try all of this at once, nothing gets finished. This order puts the biggest risk reductions first:
| Priority | Action | Why first |
|---|---|---|
| 1 | MFA for every user, phishing-resistant for admins | Stops most stolen-password attacks |
| 2 | Shrink privileged groups, separate admin accounts | Limits what one stolen login can do |
| 3 | Verified backups, including AD itself | Makes recovery possible after ransomware |
| 4 | Modern password policy and weak-password blocking | Closes the easiest way in |
| 5 | Group Policy baseline, LLMNR and share cleanup | Removes old, well-known weaknesses |
| 6 | Quarterly access reviews and offboarding routine | Keeps the result from decaying |
None of these steps is a product you buy once. Each needs someone to check it again next month, which is where most small businesses fall behind.
Where managed IT fits
The practices above are not hard to understand. They are hard to keep up with when the person responsible is an office manager or a part-time contractor with a full day job. That is the gap managed IT fills.
Axio Networks serves small and mid-sized businesses in the Phoenix metro area with managed IT services on a flat monthly rate, so budgeting is predictable and a security fix does not arrive as a surprise bill. Security is designed into every service rather than added afterward, and our average response time is under 30 minutes. For the identity side specifically, Managed Microsoft 365 covers your tenant, while endpoint security and EDR and SOC monitoring and MDR watch for the attacks described above. Risk and vulnerability assessments, and security awareness training for your staff, sit within our cybersecurity services.
If you would like to know where your own AD and Microsoft 365 setup stands against this list, talk to our team.
Our perspective
Most of the Active Directory problems we see in small businesses are not exotic. They are ordinary: an old admin account nobody remembers, a policy added years ago for a reason no one can recall, a former employee who still has access. The fix is rarely a tool. It is a routine that someone owns.
That is why we build security into the managed service itself rather than selling it as an add-on. Reviewing admin groups, checking MFA coverage, tightening Microsoft 365 and watching for suspicious sign-ins are the same job, done month after month, by a local team that knows Phoenix-area businesses and the way they work.
A flat monthly rate matters here too. When the price of good hygiene is predictable, owners actually keep doing it, instead of waiting for an incident to force a large, unplanned spend.
Jim O’Connell
FAQ
Do small businesses still need on-premises Active Directory?
Not always. If your staff mostly use Microsoft 365 and cloud apps, Entra ID may be enough, and some businesses keep a small on-premises AD only for file servers or older software. The right answer depends on the applications you run, which is worth deciding before any migration.
How often should we review Active Directory and Microsoft 365 access?
At least quarterly for admin roles, privileged groups and outside guests, and immediately whenever someone changes roles or leaves. Microsoft’s governance guidance points out that people accumulate access over time, so a fixed review date keeps it from building up unnoticed.
Should passwords expire every 90 days?
For cloud-only Microsoft 365 accounts, Microsoft recommends passwords that do not expire, with a 14-character minimum and MFA. Change a password when there is a sign of compromise rather than on a timer. Accounts governed by industry compliance rules may follow different requirements.
What is a security baseline, and do we need one?
A baseline is a vetted set of recommended settings, such as Microsoft’s GPO baselines or CISA’s Entra ID checklist. You compare your environment against it, find the gaps and adjust for what your staff actually need. It is a sound way to start, because you are not guessing which settings matter.
What is the first thing to fix if we only have a week?
Turn on MFA for every account, starting with administrators, and cut the privileged groups down to the people who truly need them. Those two changes reduce the damage from a stolen password more than anything else on this list.
Sources
- Best practices for securing Active Directory (Microsoft Learn)
- AD DS Tier Model for Privileged Access Security (Microsoft Learn)
- Best practices for Microsoft Entra roles (Microsoft Learn)
- Guidance for securing Microsoft Active Directory services (Canadian Centre for Cyber Security)
- Detecting and mitigating Active Directory compromises (Australian Signals Directorate)
- Password policy recommendations (Microsoft 365 admin)
- Microsoft Entra authentication management operations (Microsoft Learn)
- Microsoft Security Compliance Toolkit Guide (Microsoft Learn)
- Security baseline for Microsoft 365 Apps for enterprise (Microsoft Learn)
- CISA: Audit SYSVOL and remove Group Policy Preferences credentials
- CISA: Disable LLMNR
- CISA: Disable administrative shares
- CISA: Migrate from FRS to DFSR
- Zero Trust identity and device access configurations (Microsoft Learn)
- Microsoft Entra ID Governance operations reference guide (Microsoft Learn)
- Microsoft Entra ID Governance overview (Microsoft Learn)
- Entra ID SCuBA checklist (NIST NCP)
- Active Directory Forest STIG (NIST NCP)